Friday, July 30

Valve issues scathing reply over the facts behind a Steam antitrust case

Valve issues scathing reply over the facts behind a Steam antitrust case

Enlarge (credit: Getty / Aurich Lawson)

Valve has issued a scathing response to Wolfire's April lawsuit alleging anticompetitive monopoly practices on the Steam storefront. In that response, Valve argues that the suit should be dismissed because it "fails to allege the most basic elements of an antitrust case."

There’s no right to free Steam keys

Wolfire's case centers in part on the fact that Valve requires free Steam Keys generated by developers using Valve's platform to be sold on other platforms at prices no lower than those offered on Steam. But Valve argues multiple times in its filing that it has "no obligation to distribute Steam Keys, let alone to allow developers to use Steam Keys to undercut their Steam prices in other stores."

The free key system, Valve says, is intended as a way to "[give] developers a free way to sell (or give away) a reasonable number of copies of their Steam-enabled games." With that in mind, restrictions on off-Steam pricing for those keys "prevents developers from free-riding on Valve’s investment in Steam." The pricing and quantity guidelines "prevent developers from eroding large quantities of sales on Steam, which Valve bears 100% of the expense of creating and maintaining, yet provides to users for free."

Read 8 remaining paragraphs | Comments
This 900-person delta cluster in Mass. has CDC freaked out—74% are vaccinated

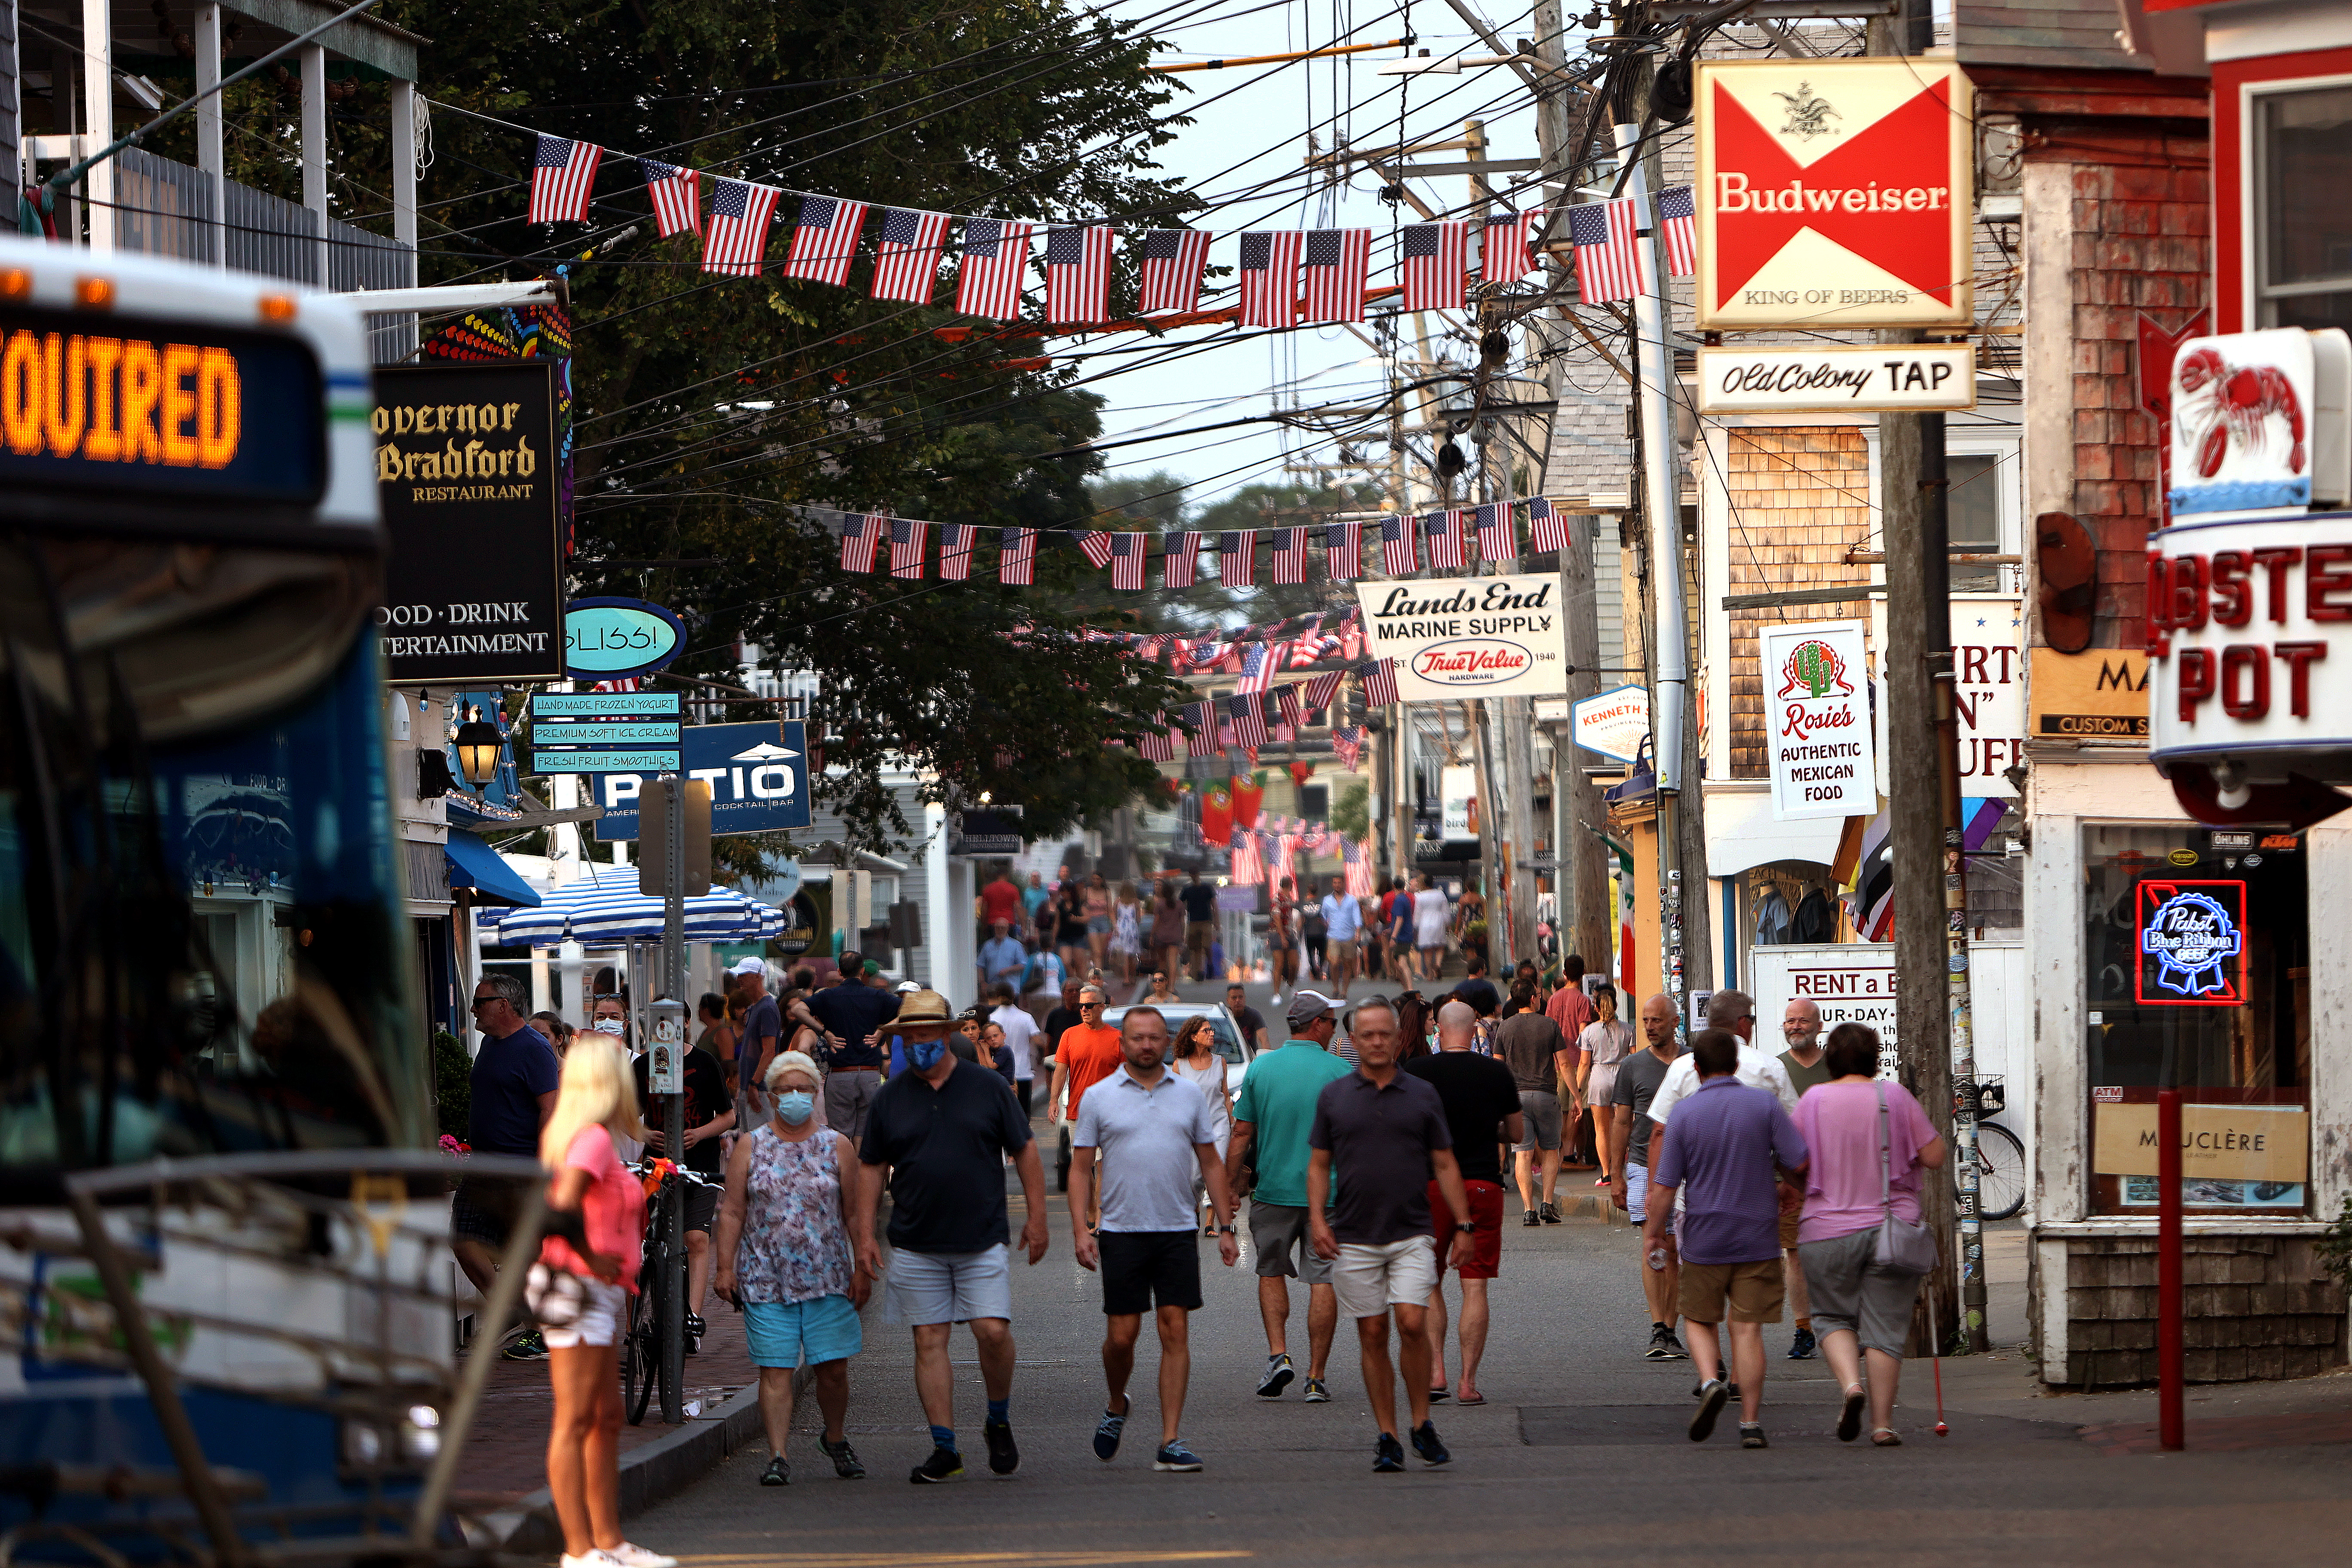
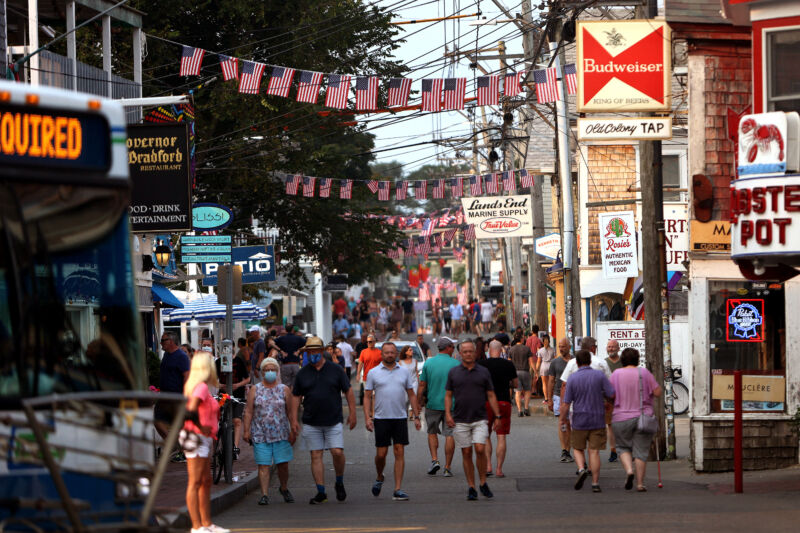
Foot traffic along Commercial Street in Provincetown, Mass., on July 20, 2021. Provincetown officials have issued a new mask-wearing advisory for indoors, regardless of vaccination status, on the latest data showing that Provincetown COVID cases are increasing.

Enlarge / Foot traffic along Commercial Street in Provincetown, Mass., on July 20, 2021. Provincetown officials have issued a new mask-wearing advisory for indoors, regardless of vaccination status, on the latest data showing that Provincetown COVID cases are increasing. (credit: Getty | Boston Globe)

An analysis of a COVID-19 cluster of around 900 people in Massachusetts—74 percent of whom are vaccinated—is among the alarming data that spurred the Centers for Disease Control and Prevention to reverse course on masks this week.

According to an internal CDC document first obtained by The Washington Post, data on the Provincetown, Massachusetts, cluster showed that vaccinated people carried surprisingly high levels of the delta coronavirus in their noses and throats. More importantly, vaccinated people were found to be spreading the dangerous virus variant to other vaccinated people. Nationwide, the CDC estimated that there are 35,000 symptomatic breakthrough infections per week among 162 million fully vaccinated Americans.

The CDC document overall highlights that delta is extremely contagious—much more so than previous versions of the virus, as well as the common cold or even the seasonal flu. Delta is more in line with the contagiousness of chickenpox, the CDC document said.

Read 4 remaining paragraphs | Comments

America’s favorite truck goes hybrid: The Ford F-150, reviewed


Ford’s F-series pickup trucks have been the best-selling vehicles in the United States for what seems like forever, so there's probably a powerful temptation not to mess with something that has worked so well. But the times, they are a-changin’, and so must pickup trucks.

Ford revealed its new ideas in the form of the all-electric 2022 F-150 Lightning this past spring, but there’s another new option for those who want to go green(er) but aren’t willing to give up burning hydrocarbons to get around: the F-150 PowerBoost hybrid. While the hybrid is not a game-changer, it offers better mileage and the ability to use it as a 7.2 kW generator—even while the vehicle is in motion.

Read 12 remaining paragraphs | Comments

Software downloaded 30,000 times from PyPI ransacked developers’ machines

Software downloaded 30,000 times from PyPI ransacked developers’ machines

Enlarge

Open source packages downloaded an estimated 30,000 times from the PyPI open source repository contained malicious code that surreptitiously stole credit card data and login credentials and injected malicious code on infected machines, researchers said on Thursday.

In a post, researchers Andrey Polkovnichenko, Omer Kaspi, and Shachar Menashe of security firm JFrog said they recently found eight packages in PyPI that carried out a range of malicious activity. Based on searches on https://pepy.tech, a site that provides download stats for Python packages, the researchers estimate the malicious packages were downloaded about 30,000 times.

Systemic threat

The discovery is the latest in a long line of attacks in recent years that abuse the receptivity of open source repositories, which millions of software developers rely on daily. Despite their crucial role, repositories often lack robust security and vetting controls, a weakness that has the potential to cause serious supply chain attacks when developers unknowingly infect themselves or fold malicious code into the software they publish.

Read 14 remaining paragraphs | Comments

New bank-fraud malware called Vultur infects thousands of devices

New bank-fraud malware called Vultur infects thousands of devices

Enlarge (credit: Getty Images)

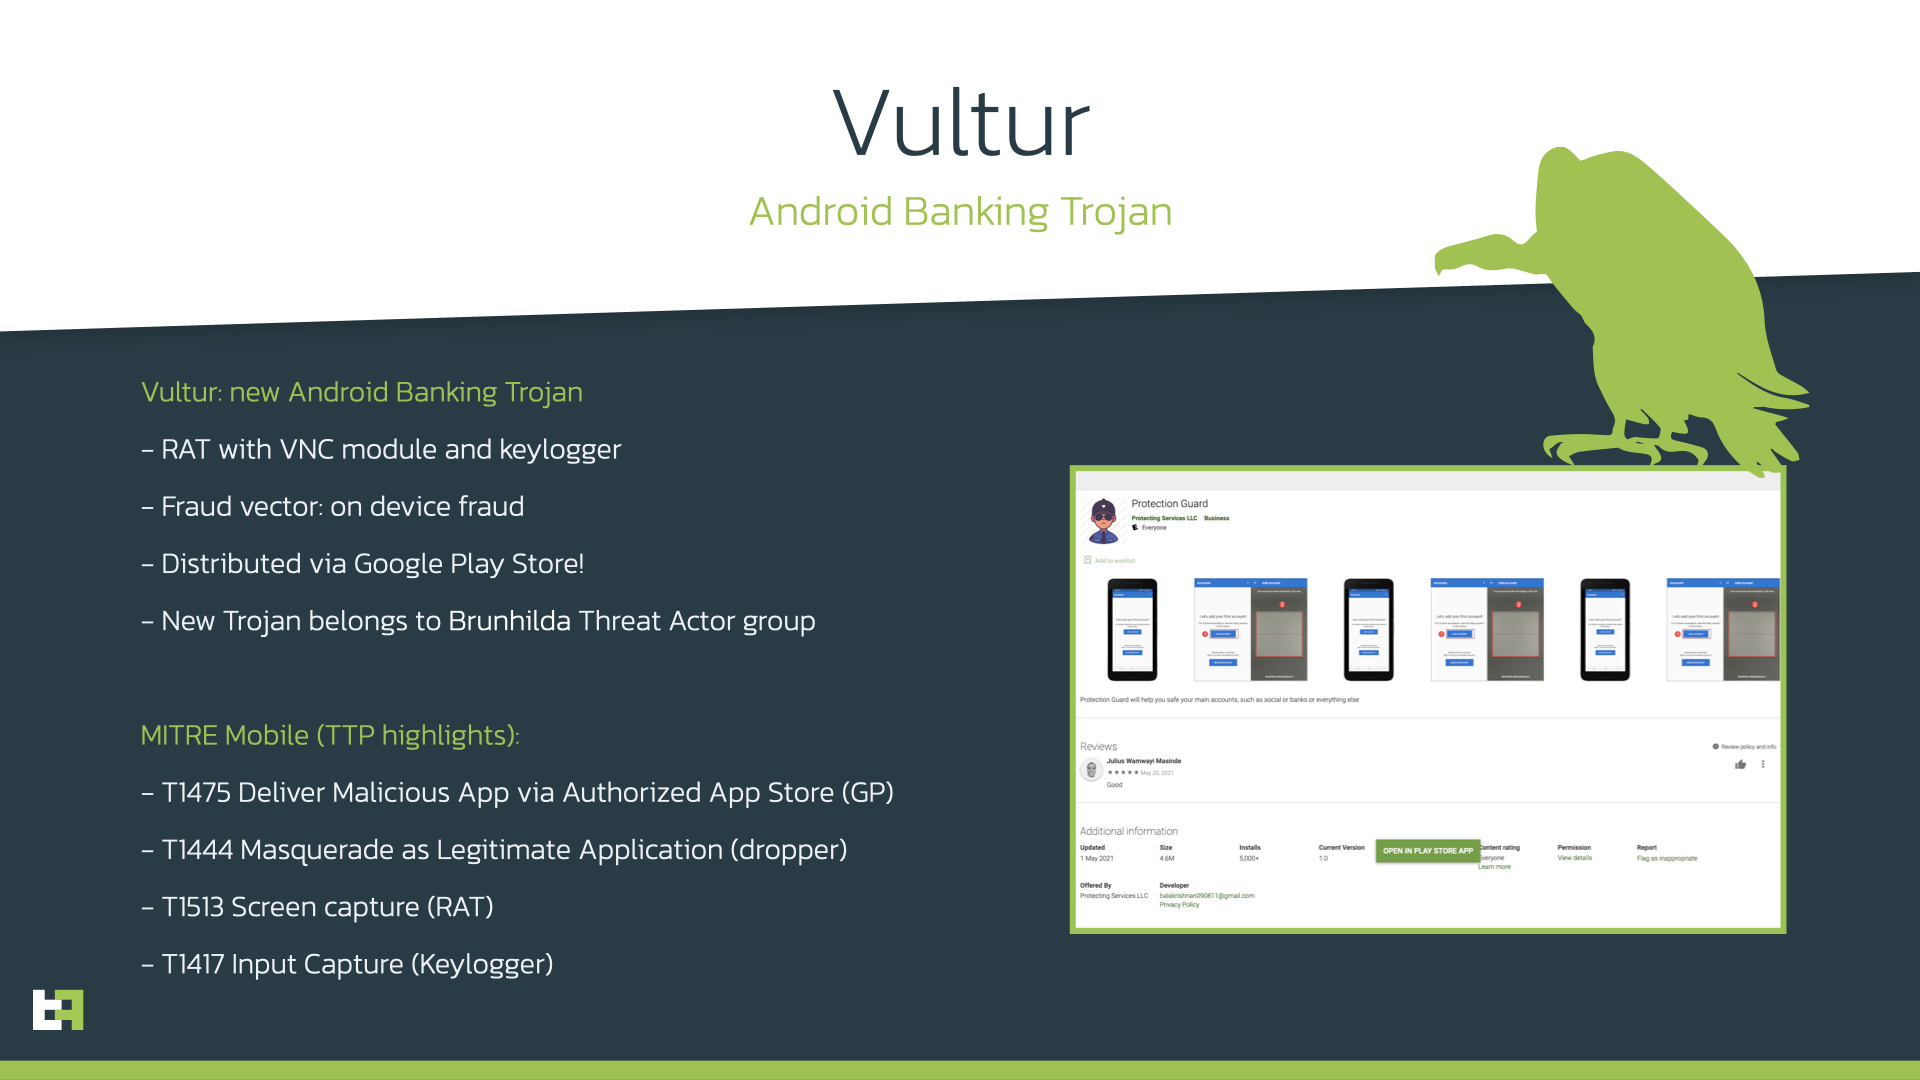
Recently detected Android malware, some spread through the Google Play Store, uses a novel way to supercharge the harvesting of login credentials from more than 100 banking and cryptocurrency applications.

The malware, which researchers from Amsterdam-based security firm ThreatFabric are calling Vultur, is among the first Android threats to record a device screen whenever one of the targeted apps is opened. Vultur uses a real implementation of the VNC screen-sharing application to mirror the screen of the infected device to an attacker-controlled server, researchers with ThreatFabric said.

(credit: ThreatFabric)

(credit: ThreatFabric)

The next level

The typical modus operandi for Android-based bank-fraud malware is to superimpose a window on top of the login screen presented by a targeted app. The “overlay,” as such windows are usually called, appears identical to the user interface of the banking app, giving victims the impression they’re entering their credentials into a trusted piece of software. Attackers then harvest the credentials, enter them into the app running on a different device, and withdraw money.

Read 12 remaining paragraphs | Comments

Rocket Report: Ariane V returns after long layoff, Rocket Lab’s tough culture

Artist's conception of cutting-edge rockets.

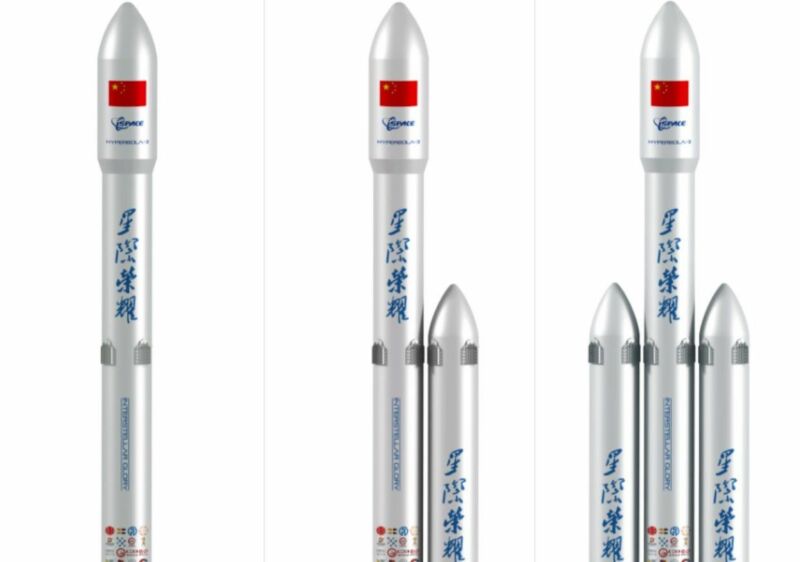
Enlarge / China's iSpace releases renderings of a 1-, 2-, and 3-core Hyperbola-3 rocket. (credit: iSpace/Andrew Jones/Twitter)

Welcome to Edition 4.09 of the Rocket Report! I was certainly looking forward to the second launch of Boeing's Starliner spacecraft on Friday, and the Atlas V rocket was ready to go. Alas, serious problems with Russia's new space station module, Nauka, delayed the launch until next Tuesday.

As always, we welcome reader submissions, and if you don't want to miss an issue, please subscribe using the box below (the form will not appear on AMP-enabled versions of the site). Each report will include information on small-, medium-, and heavy-lift rockets as well as a quick look ahead at the next three launches on the calendar.

New Zealand publication investigates Rocket Lab work culture. Former employees of launch company Rocket Lab claim that, behind its flashy public relations, is a toxic culture of fear where people are pushed out of the business and punished for minor transgressions, BusinessDesk reports. The article asserts that founder Peter Beck is an inspirational leader but that his management style is more appropriate for a very small startup rather than a maturing aerospace company. Although Rocket Lab is based it the US, it operates a rocket assembly and launch site in New Zealand.

Read 28 remaining paragraphs | Comments
Russian module suddenly fires thrusters after docking with space station

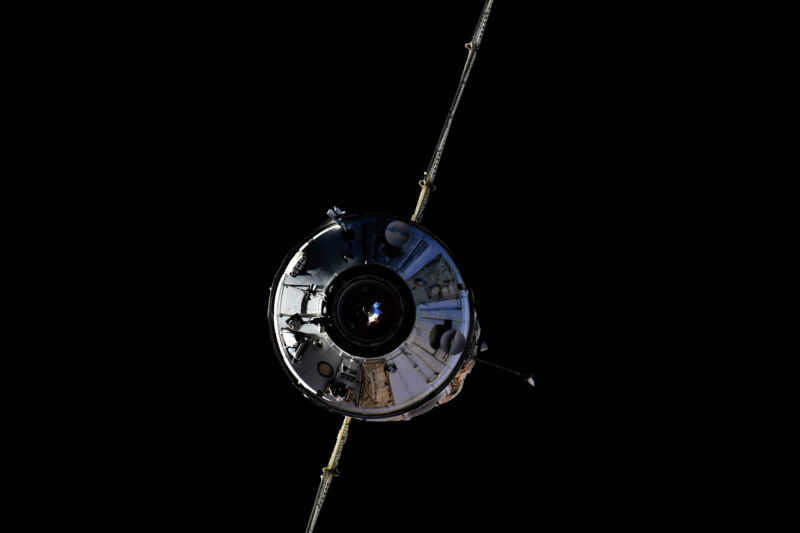
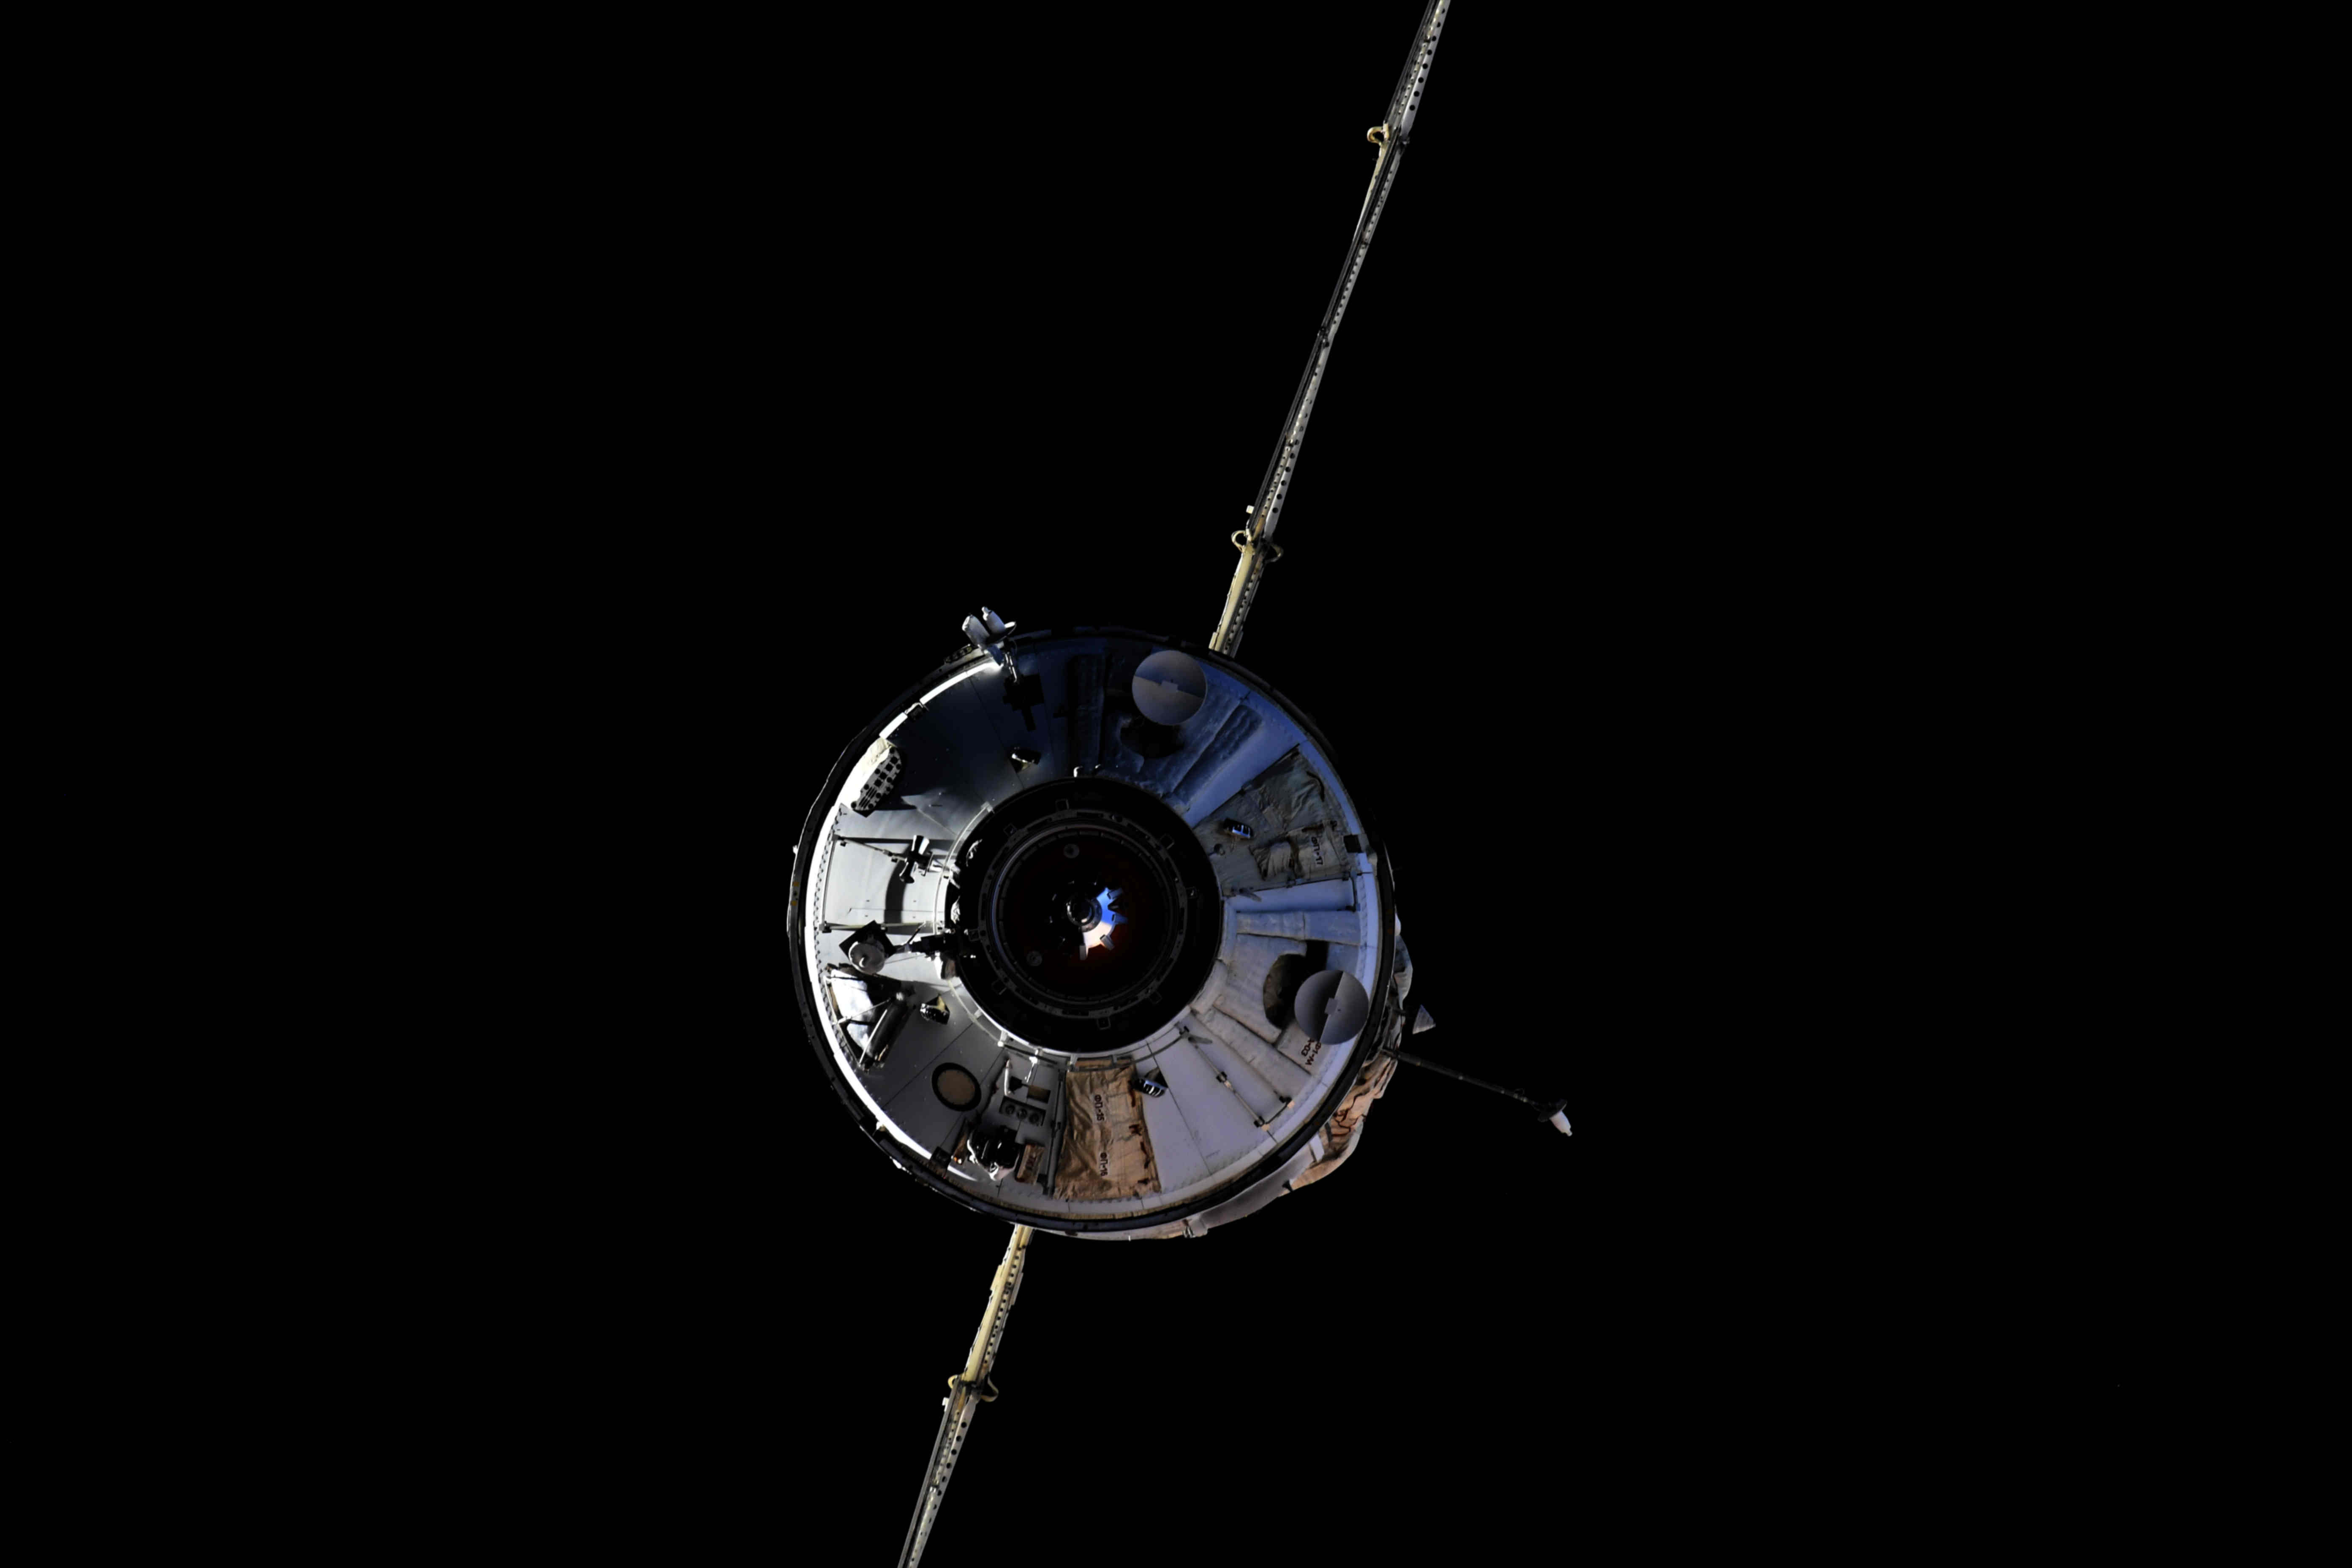
A silver-grey module moves through the terrifying blackness of outer space.

Enlarge / Russian "Nauka" module approaches the International Space Station. (credit: Roscosmos)

Flight controllers at NASA and Roscosmos averted a disaster on Thursday after a large Russian module docked with the International Space Station and began to "inadvertently" fire its thrusters.

The Russian "Nauka" module linked to the space station at 8:30 am CT (13:30 UTC), local time in Houston, where NASA's Mission Control is based. After that, Russian cosmonauts aboard the station began preparing to open the hatches leading to Nauka, but at 11:34 am Houston time, Nauka unexpectedly started to fire its movement thrusters.

Within minutes, the space station began to lose attitude control. This was a problem for several reasons. First of all, the station requires a certain attitude to maintain signal with geostationary satellites and talk to Mission Control on the ground. Also, solar arrays are positioned to collect power based upon this predetermined attitude.

Read 10 remaining paragraphs | Comments