Friday, October 30

This Week in Security: Discord, Chromium, and WordPress Forced Updates

[Masato Kinugawa] found a series of bugs that, when strung together, allowed remote code execution in the Discord desktop app. Discord’s desktop application is an Electron powered app, meaning it’s a web page rendered on a bundled light-weight browser. Building your desktop apps on JavaScript certainly makes life easier for developers, but it also means that you inherit all the problems from running a browser and JS. There’s a joke in there about finally achieving full-stack JavaScript.

The big security problem with Electron is that a simple Cross Site Scripting (XSS) bug is suddenly running in the context of the desktop, instead of the browser. Yes, there is a sandboxing option, but that has to be manually enabled.

And that brings us to the first bug. Neither the sandbox nor the contextIsolation options were set, and so both defaulted to false. What does this setting allow an attacker to do? Because the front-end and back-end JavaScript runs in the same context, it’s possible for an XSS attack to override JS functions. If those functions are then called by the back-end, they have full access to Node.js functions, including exec(), at which point the escape is complete.

Now that we know how to escape Electron’s web browser, what can we use for an XSS attack? The answer is automatic iframe embeds. For an example, just take a look at the exploit demo below. On the back-end, all I have to do is paste in the YouTube link, and the WordPress editor does its magic, automatically embedding the video in an iframe. Discord does the same thing for a handful of different services, one being Sketchfab.

This brings us to vulnerability #2. Sketchfab embeds have an XSS vulnerability. A specially crafted sketchfab file can run some JS whenever a user interacts with the embedded player, which can be shoehorned into discord. We’re almost there, but there is still a problem remaining. This code is running in the context of an iframe, not the primary thread, so we still can’t override functions for a full escape. To actually get a full RCE, we need to trigger a navigation to a malicious URL in the primary pageview, and not just the iframe. There’s already code to prevent an iframe from redirecting the top page, so this RCE is a bust, right?

Enter bug #3. If the top page and the iframe are on different domains, the code preventing navigation never fires. In this case, JavaScript running in an iframe can redirect the top page to a malicious site, which can then override core JS functions, leading to a full escape to RCE.

It’s a very clever chaining of vulnerabilities, from the Discord app, to an XSS in Sketchfab, to a bug within Electron itself. While this particular example required interacting with the embedded iframe, it’s quite possible that another vulnerable service has an XSS bug that doesn’t require interaction. In any case, if you use Discord on the desktop, make sure the app is up to date. And then, enjoy the demo of the attack, embedded below.

Chromium Freetype Overflow

Chromium 86 has a fix for a particularly nasty bug. Tracked as CVE-2020-15999, this is a bug in how FreeType fonts are rendered. Now that Microsoft has switched to Edgium (Chromium powered Edge), we get two-for-one deals on Chromium vulnerabilities. This bug is interesting because it’s reportedly being actively exploited already. Google has marked the bug public, so we can take a closer look at exactly what happened.

The problem is in the FreeType library, regarding how fonts are handled when they contain embedded PNGs. To put it simply, the PNG width and height are stored in the font as 32-bit values, but those values are truncated to 16-bit before the buffer is allocated. After this, the PNG is copied to the buffer, but using the non-truncated values. A check is then performed to make sure the copy didn’t overflow, but unhelpfully, this was checked *after* the copy had taken place. The bug includes a test case, so feel free to go check your devices using that code. It’s not clear how long this bug has existed, but it’s possible it also affects Android’s System WebView, which is much slower to update.

Step-by-step of Chrome Exploit

[Man Yue Mo] recently published a detailed report on a Use-After-Free Chrome bug he discovered back in March, tracked as CVE-2020-6449. What makes this one worth looking at is the detailed account he gives us of the process of developing a working exploit from the bug. The whole account is a masterclass in abusing JavaScript to manipulate the state of the underlying engine. As a bonus, he gives us a link to the PoC exploit code to look at, too.

FBI Warning

The FBI, along with CISA and HHS, has issued a warning (PDF) about an ongoing redoubling of ransomware attacks against US hospitals and other healthcare providers. This attack is using the Trickbot malware and the Ryuk ransomware. They also note the use of DNS tunneling for data exfiltration, and specifically mention Point of Sale systems as a target.

The mitigation steps are particularly interesting in trying to read between the lines here. Before we look too deeply, I have to call out an outdated piece of advice: “Regularly change passwords”. This has been the bane of many users and administrators, and leads to weaker security, not stronger. With that out of the way, let’s look at the other recommendations.

A few recommendations are boiler-plate, like two-factor authentication, install security updates, have backups, etc. I was surprised to see the recommendation to allow local administration, in order to get things working again. What might be the most interesting is the recommendation to take a hard look at any RDP services that are running. Does this mean that some healthcare PoS system is running an out-of-date Windows, with a vulnerable RDP service open to the network by default, and it’s suddenly being targeted? Maybe. I’ve learned not to put too much stock in these advisories, unless actual details are given, and this particular example is quite light on details.

Loginizer’s SQL Injection

The popular Loginizer WordPress plugin is intended to protect your site’s login page from attack. It can add two-factor authentication, CAPTCHAs for repeated login attempts, and even detect brute-force attempts and blacklist the offending IP. That last one is where the problem lies. Incoming login attempts are logged to a SQL database, and that logging wasn’t properly sanitized, nor were prepared statements used. Because of this, the login page was subject to a very simple SQL injection attack. The Lesson? Sanitize your inputs, and use prepared statements! The latest update fixes this, as well as a separate but similar security issue.

What makes this bug novel is that WordPress found it a big enough problem to break the glass and push the big red button labeled “Force Update”. I didn’t know the folks at WordPress had a button that did that, but for particularly bad bugs like this one, it’s a useful capability. A few users complained that this update was installed even though they had auto-updates disabled. It’s a fine line to walk here, but it seems like WordPress should make it clear in the settings that this feature exists, and include a way to opt-out of forced updates like this one.
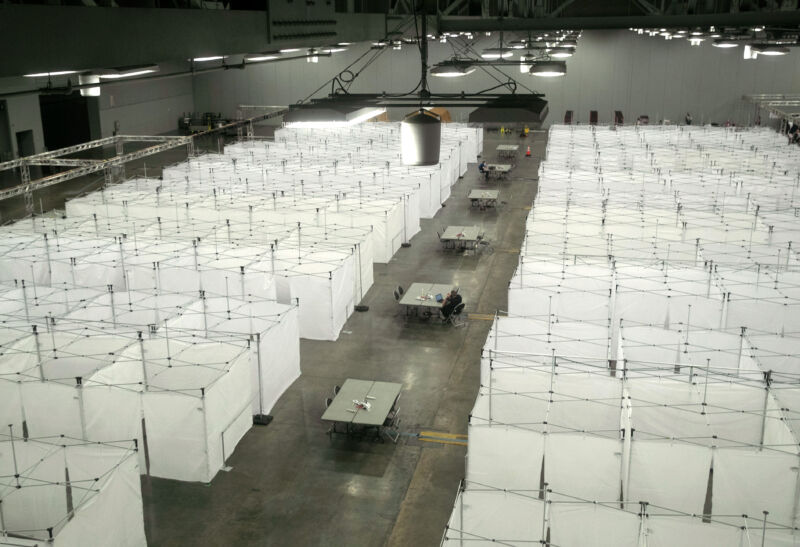
US logs nearly 90,000 new coronavirus cases Thursday, 1 new case per second

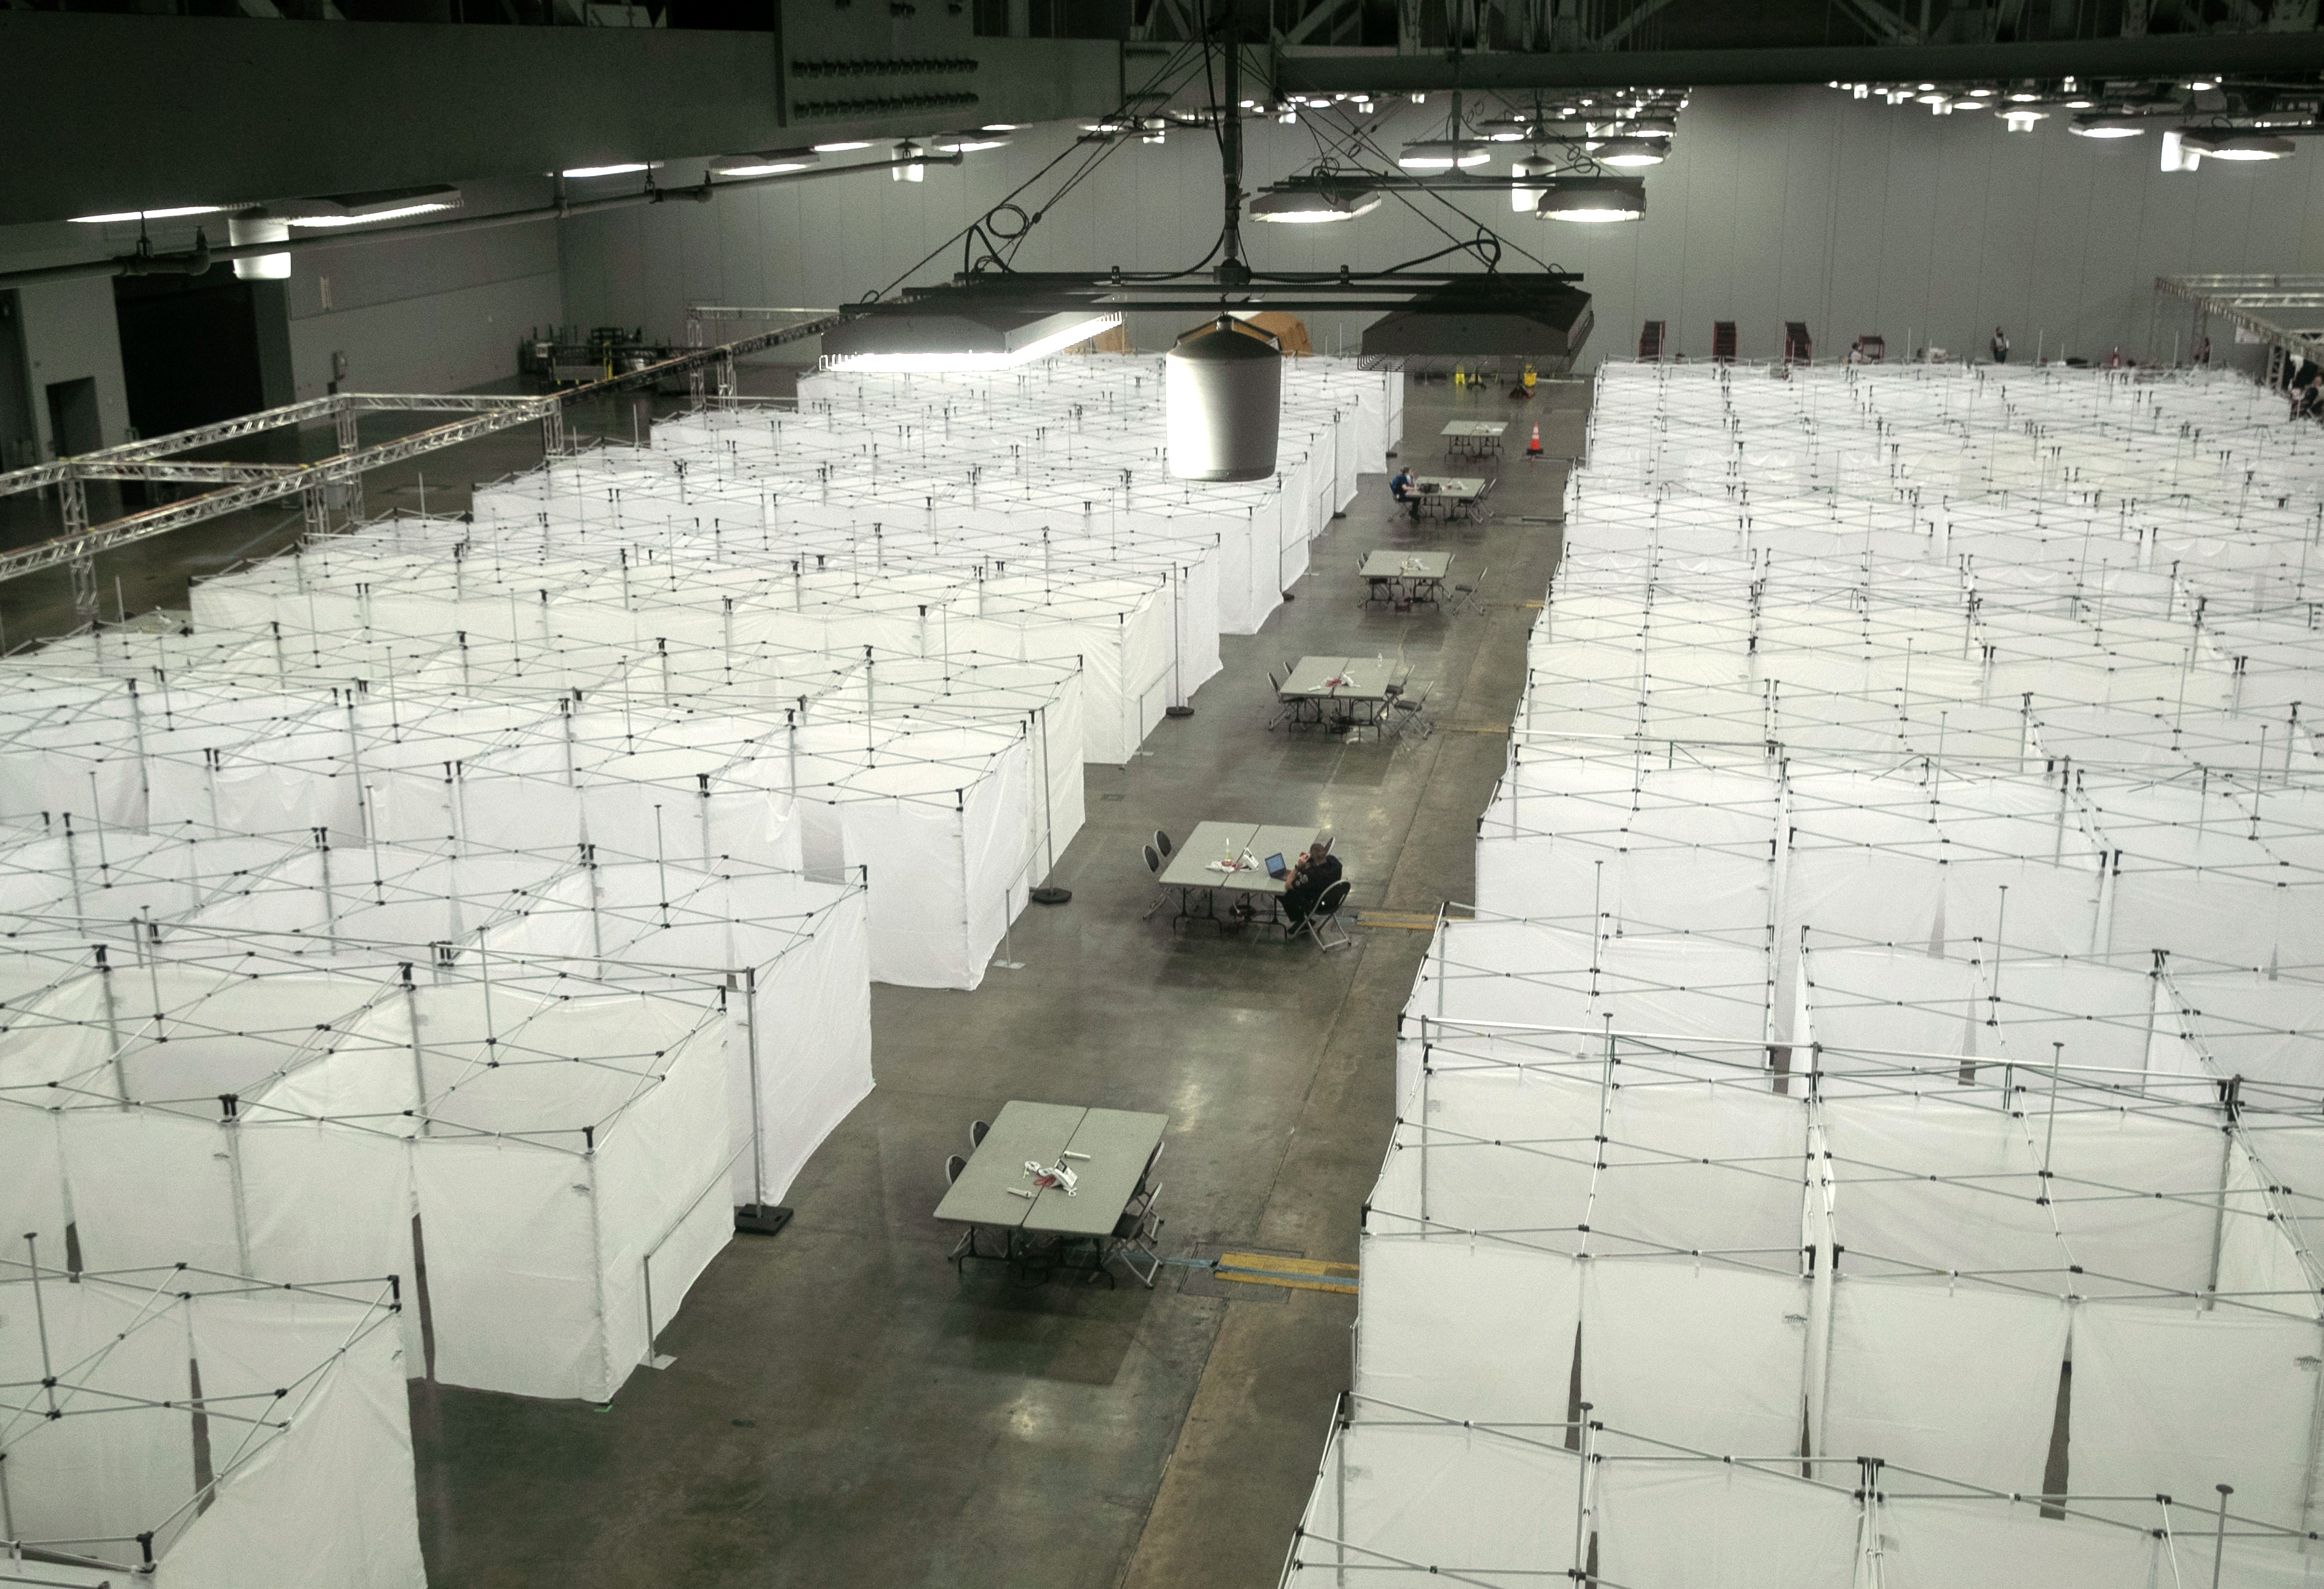
Some 250 Covid-19 isolation bays stand at the ready at the Austin Convention Center on August 07, 2020 in Austin, Texas. The cavernous facility was prepared for use as a field hospital for Covid-19 patients.

Enlarge / Some 250 Covid-19 isolation bays stand at the ready at the Austin Convention Center on August 07, 2020 in Austin, Texas. The cavernous facility was prepared for use as a field hospital for Covid-19 patients. (credit: Getty | John Moore)

The United States recorded nearly 90,000 new coronavirus cases Thursday, the largest single-day total yet in the pandemic.

The record-breaking day comes amid a steady and sharp climb in US cases. The country is experiencing the third and highest peak in cases, and it’s unclear how high the numbers will go. Today may well be another record-breaking day. The country’s seven-day rolling average of daily new cases is now over 76,000, another record in the pandemic.

With more than 88,400 cases Thursday, the US is expected to easily surpass 9 million cases total Friday. Deaths are likely to near 30,000.

Read 5 remaining paragraphs | Comments

Solve coding challenges at Runcode.ninja online competition, Nov. 6-9

Shozoku and ninjato are encouraged, but not strictly required, in order to compete.

Enlarge / Shozoku and ninjato are encouraged, but not strictly required, in order to compete. (credit: RunCode)

Annual programming competition Runcode.ninja is back again in its fourth year, beginning Friday, November 6. RunCode is a nonprofit organization staffed by volunteers working in their spare time and focused on providing educational opportunities for coders and infosec folks. The online event allows programmers of all experience levels to tackle a wide array of challenges, using any of 14 supported programming languages.

This year, the competition theme is "all things web"—which means that most challenges will have something to do with websites; although the "something" can vary pretty drastically, from user interaction to server log analysis. The event will have more than 30 available challenges, grouped into easy, intermediate, and hard, for competitors to find and upload solutions for.

For each challenge, competitors will be given a problem description, a sample data set, and an expected output to make the desired order and formatting clear. Competitors are expected to generate more test data of their own and thoroughly verify the correctness of their code against all the corner cases they can think of; solutions tested against only the sample data provided will likely fail the challenge. Uploaded code is run in a sandboxed Docker container and its output tested for correctness.

Read 1 remaining paragraphs | Comments

Monster Mash: These are the best new horror movies to binge this Halloween

Halloween weekend is the perfect time to check out some of the best horror films released in October.

Enlarge / Halloween weekend is the perfect time to check out some of the best horror films released in October. (credit: Photo collage by Aurich Lawson)

It's Halloween weekend, and with the ongoing pandemic putting a kibosh on the usual large parties and gatherings, it's the perfect opportunity to order in and binge-watch horror movies. There are plenty of classic films to choose from, but if you're keen to discover something new, October has been a remarkably good month for solidly entertaining indie horror comedies, along with a handful of films that fall under a rubric I'd call "prestige horror." And for once there's not a zombie in sight; we've got vampires, werewolves, and mutant monsters running amok instead, along with some really bad hair.

(Some mild spoilers below but no major reveals.)

Seven years after a global apocalypse, a young man braves 85 miles of mutant man-eating monsters to reunite with his high school girlfriend in Love and Monsters.

Love and Monsters

Read 26 remaining paragraphs | Comments

“Oh Jeeeesus”: Drivers react to Tesla’s full self-driving beta release

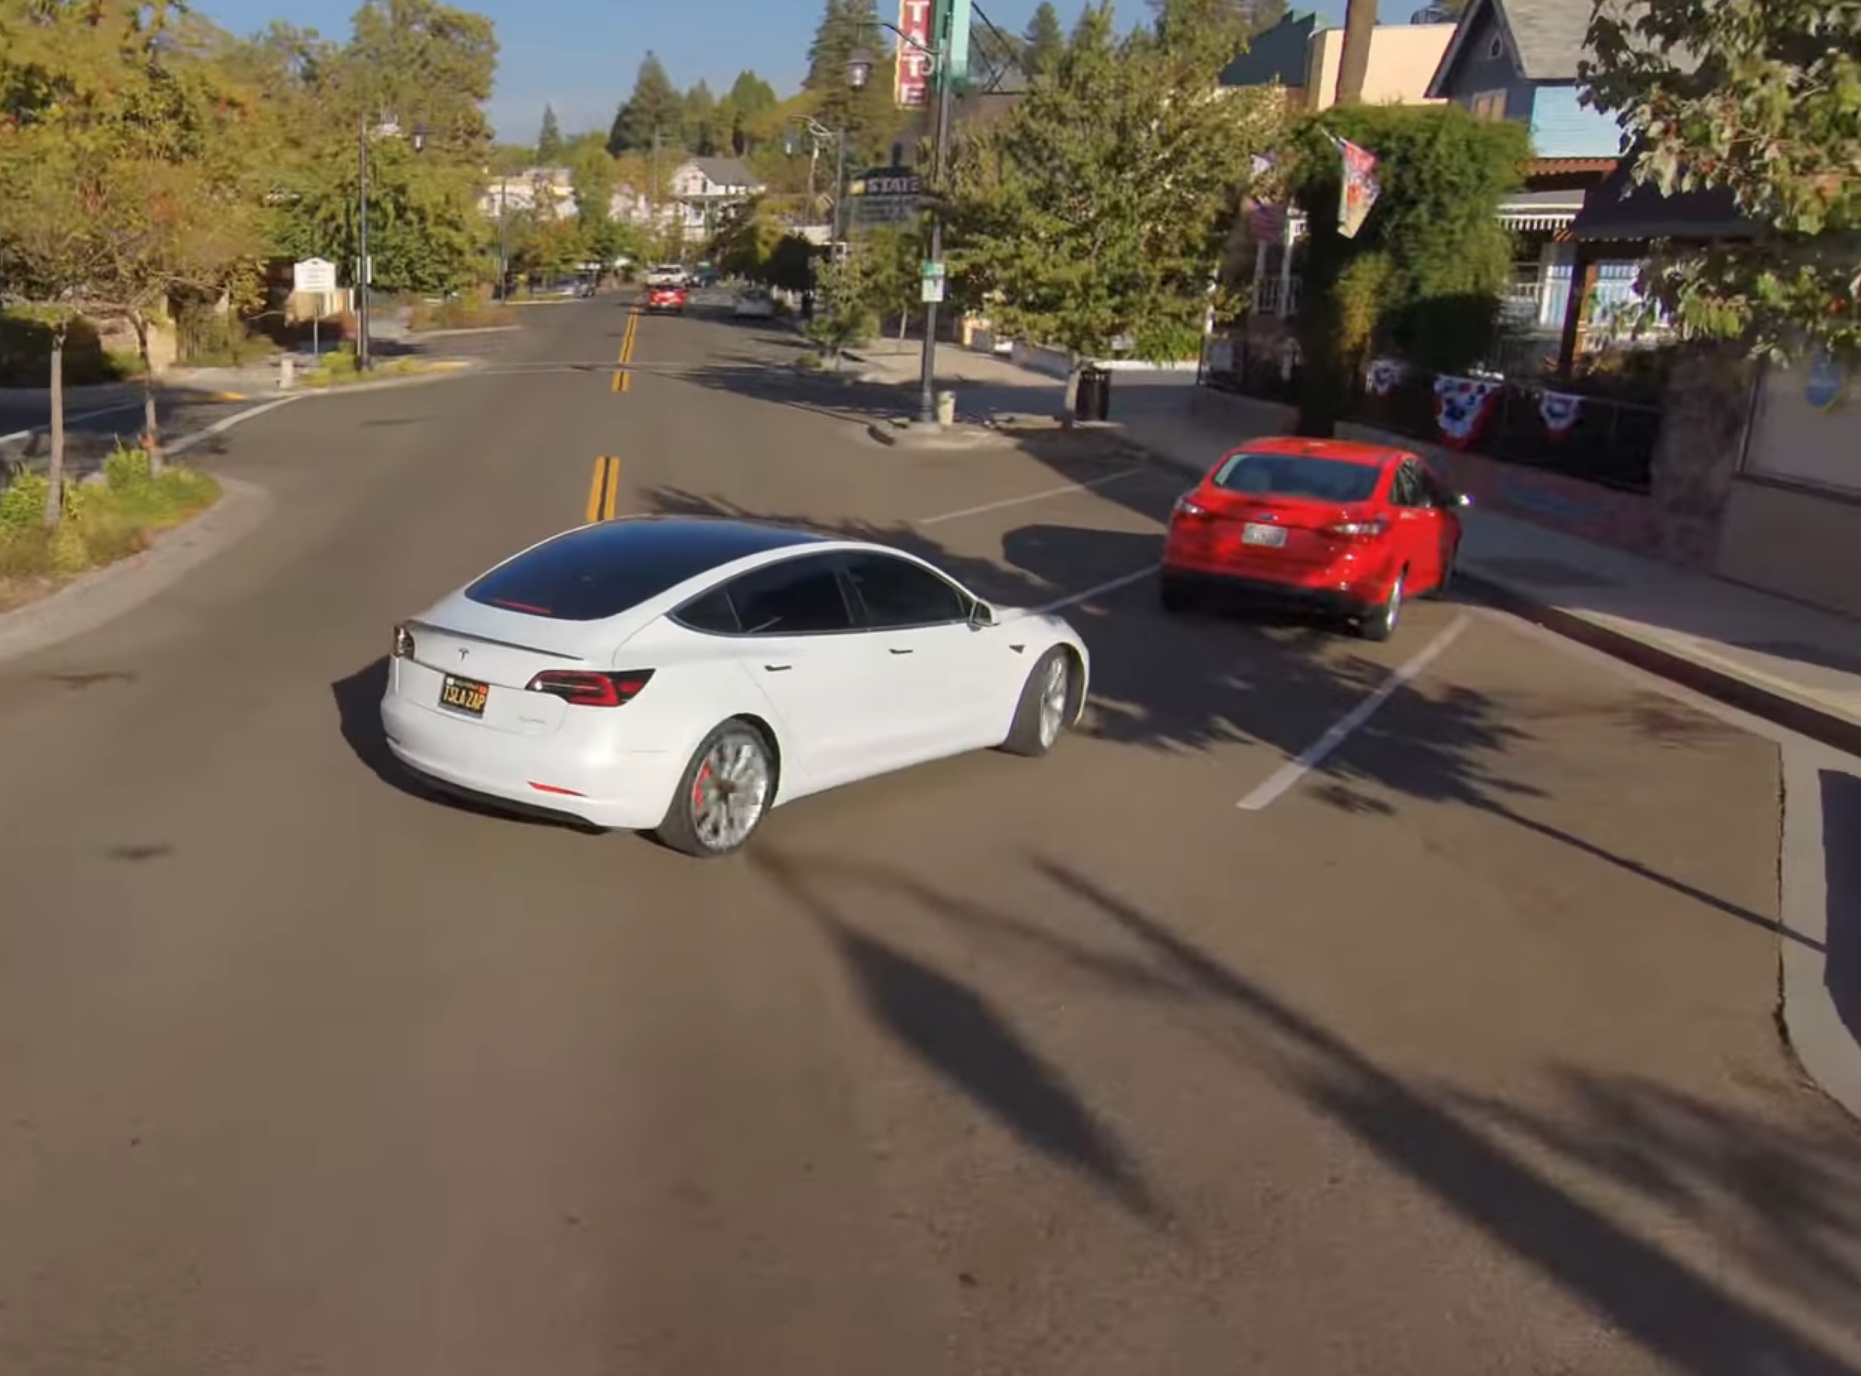
Two cars nearly collide in a parking lot.

Enlarge / YouTuber Brandon M captured this drone footage of his Tesla steering toward a parked car. "Oh Jeeeesus," he said as he grabbed the steering wheel. (credit: Brandon M)

Last week, Tesla released an early version of its long-awaited "full self-driving" software to a limited number of customers. It was arguably Tesla's biggest Autopilot update ever. The software enables Tesla vehicles to autonomously navigate the vast majority of common roadway situations and complete many trips from start to finish.

Tesla considers it to be beta software and says it's not intended for fully autonomous operation. Drivers are expected to keep their eyes on the road and hands on the wheel at all times.

To understand the new software, I watched more than three hours of driving footage from three Tesla owners who got the FSD update. These YouTube videos underscored how important it is for drivers to actively supervise Tesla's new software. Over the course of three hours, the drivers took control more than a dozen times, including at least two cases when the car seemed to be on the verge of crashing into another vehicle.

Read 23 remaining paragraphs | Comments

Color E-Ink Display Photo Frame Pranks [Mom]

As a general rule, it’s not nice to prank your mother. Moms have a way of exacting subtle revenge, generally in the form of guilt. That’s not to say it might not be worth the effort, especially when the prank is actually wrapped in a nice gesture, like this ever-changing e-paper family photo frame.

The idea the [CNLohr] had was made possible by a new generation of multicolor e-paper displays by Waveshare. The display [Charles] chose was a generous 5.65″ unit with a total of seven colors. A little hacking revealed an eighth color was possible, adding a little more depth to the images. The pictures need a little pre-processing first, of course — dithering to accommodate the limited palette — but look surprisingly good on the display. They have a sort of stylized look, as if they were printed on a textured paper with muted inks.

The prank idea was simple — present [Mrs. Lohr] with a cherished family photo to display, only to find out that it had changed to another photo overnight. The gaslighting attempt required a bit more hacking, including some neat tricks to keep the power consumption very low. It was also a bit of a squeeze to get it into a frame that was slim enough not to arouse suspicion. The video below details some of the challenges involved in this build.

In the end, [Mom] wasn’t tricked, but she still seemed pleased with the final product. These displays seem like they could be a lot of fun — perhaps a version of the very-slow-motion player but for color movies would be doable.

Rocket Report: SpaceX hits the century mark, Vote for Atlas V on Election Day

Photograph of a rocket just after liftoff on a cloudy day.

Enlarge / The "In Focus" mission takes to the skies this week. (credit: Rocket Lab)

Welcome to Edition 3.22 of the Rocket Report! After a spate of recent scrubs, the Cape gets down to business in the coming week with back-to-back government launches, one by United Launch Alliance and the other by SpaceX. Fingers (and toes) are crossed.

As always, we welcome reader submissions, and if you don't want to miss an issue, please subscribe using the box below (the form will not appear on AMP-enabled versions of the site). Each report will include information on small-, medium-, and heavy-lift rockets as well as a quick look ahead at the next three launches on the calendar.

Rocket Lab orbits its 15th mission. Rocket Lab successfully launched its 15th Electron mission and deployed Earth-imaging satellites for Planet and Spaceflight Inc. customer Canon Electronics, the company said. The "In Focus" mission launched from Rocket Lab Launch Complex 1 on New Zealand's Māhia Peninsula at 21:21 UTC Wednesday.

Read 26 remaining paragraphs | Comments